
 US
 IN
 UK


 featured
Executive Certificate Course (Live Classes) , Certificate Programme
iHUB DivyaSampark, IIT Roorkee & SkillArbitrage jointly present: Advanced Certification in Global Data Protection, Privacy Engineering & AI Governance
 Duration - 6 Month, 8-10 hours/week
 Course fee: - INR 1,55,000 + GST
About the Collaboration: iHUB DivyaSampark, IIT Roorkee & SkillArbitrage
Certification
This course is offered in collaboration between iHUB DivyaSampark, IIT Roorkee, a Technology Innovation Hub under the National Mission on Interdisciplinary Cyber-Physical Systems (NM-ICPS) by the Department of Science and Technology, Government of India, and SkillArbitrage.
Participants who successfully complete the program will receive a co-branded certificate from SkillArbitrage and iHUB DivyaSampark, IIT Roorkee.
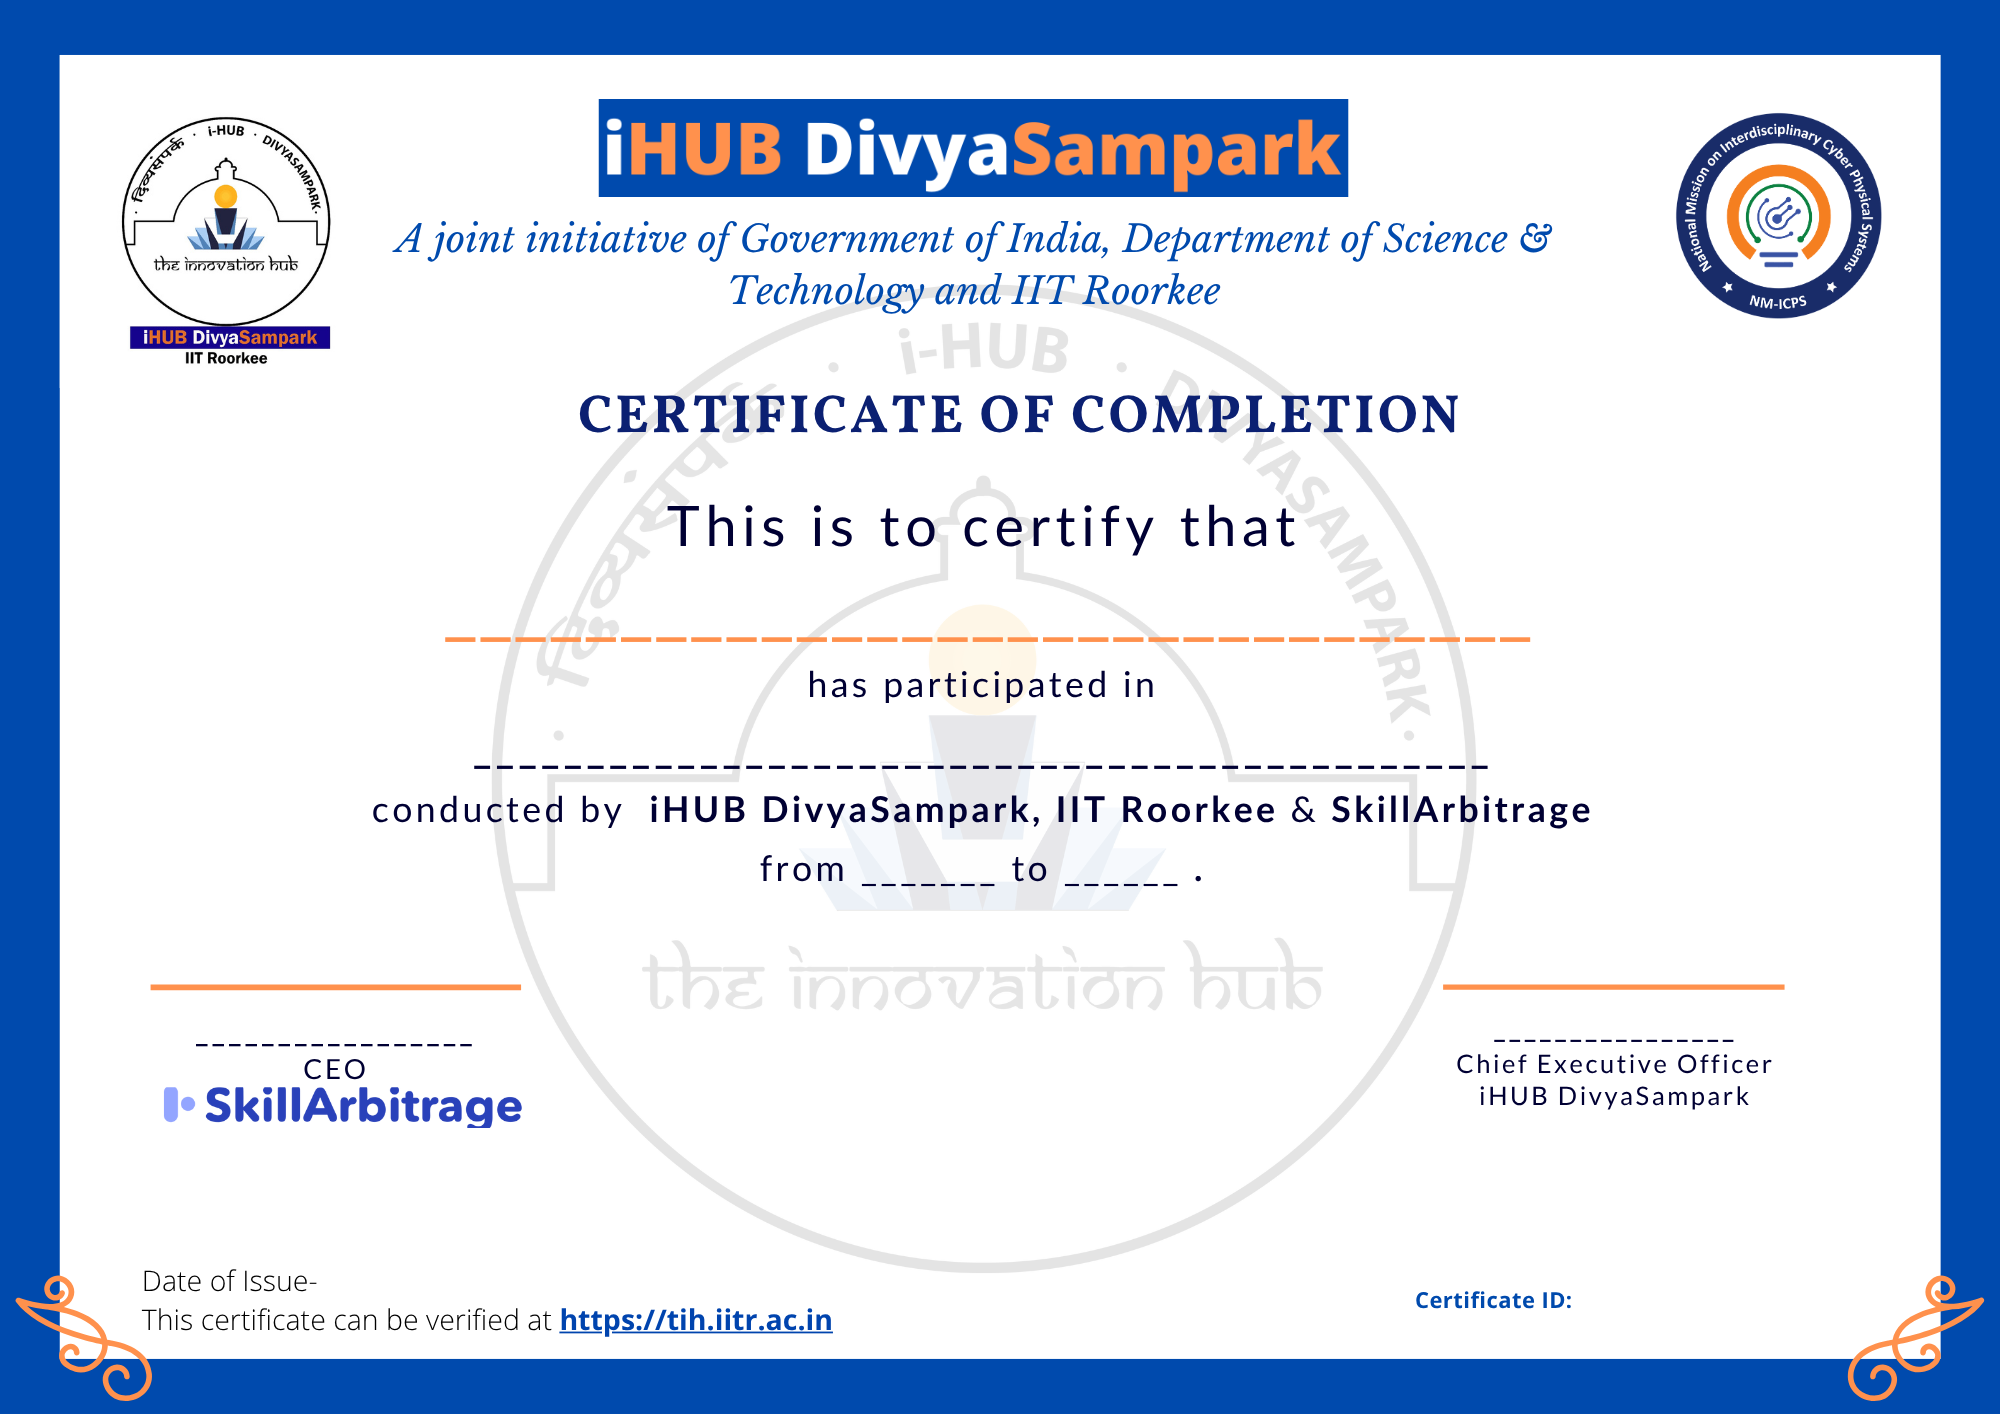
(Certificate Disclaimer: Only for illustration purposes)
Who Should Take This Course?
This course is designed for ambitious individuals who want to build genuine, employer-relevant data protection and privacy skills at the intersection of law, technology, and organisational governance:
Legal & Compliance Professionals — lawyers, company secretaries, and compliance officers who want to move beyond policy documents into technical privacy implementation, regulatory strategy, and data-driven governance.
IT & Security Professionals — developers, security engineers, and IT professionals who want to enter data protection; the Privacy Engineering track adds regulatory knowledge, governance frameworks, and legal context to your existing technical skills.
Risk & Governance Professionals — risk analysts, auditors, and governance professionals who want to specialise in privacy risk management, DPIAs, and organisation-wide data governance.
Data Protection Aspirants & Law/Engineering Graduates — graduates targeting DPO, privacy counsel, or privacy engineering roles, looking to build the combination of law, technology, governance, and portfolio that employers test for.
Fresh Graduates & Students — LL.B., B.Tech, M.Tech, and MBA students in law, engineering, computer science, or business who want to enter data protection with a skill set and portfolio most candidates lack.
Career Switchers with Analytical or Legal Backgrounds — paralegals, auditors, risk analysts, or anyone with strong analytical or legal foundations looking to pivot into data protection and privacy.
International students can apply for the program, provided they meet the eligibility criteria set for the course.
What Will You Learn from This Course?
Career Potential After This Course
- After completing this course, you can work with:
- Multinational Corporations and Law Firms — as an in-house Data Protection Officer or Privacy Counsel.
- Technology, Fintech, and Healthcare Companies — as a Privacy Engineer or Technical Compliance specialist.
- Banks and Financial Institutions — as a Privacy Risk Analyst or Governance specialist.
- Consulting Firms, Auditors, and Advisory Practices — as a Data Governance & Compliance Consultant.
- Regulators and Technology Companies — applying your understanding of frameworks like GDPR, the DPDP Act, and CCPA/CPRA in a policy, enforcement, or platform-governance context.
Training Methodology

Online 24/7 Access
Study materials available via the LMS and via Android & iOS apps.
Practical Case Studies
Real-world case studies, breach-response scenarios, and DPO-style judgment calls built into every module.
Live Online Classes
1 live class per week, plus 2 practical exercises weekly, covering theory and hands-on implementation, with recording access so you can learn at your own pace.
Convenient Class Timings
Classes held after work hours, typically on Sundays or after 8 PM on weekdays — complete the program while you work.
Live Doubt Clearing
Unlimited one-on-one doubt-clearing sessions with mentors and instructors.
Optional Campus Immersion
Optional Campus Immersion: Optional campus visit and networking sessions at IIT Roorkee campus .
What Makes This Course Unique?
- Joint Program by iHUB DivyaSampark, IIT Roorkee and SkillArbitrage: a Technology Innovation Hub backed by the Department of Science and Technology, Government of India, and a career-focused edtech platform, delivering industry-aligned training in data protection and privacy.
- Three Specialisation Tracks: go deep on Privacy Engineering, Data Protection Law & Regulatory Compliance, or Privacy Governance, Risk & Data Ethics — while staying literate across all three.
- Skills-First, Rigour-First Design: every concept backed by working, reviewed frameworks and real case studies — no hand-waving, no toy examples.
- Audit-Ready Compliance Discipline: learn why most compliance programs and DPIAs collapse under real scrutiny, and how to build ones that hold up.
- AI Governance Integrated Throughout: AI accountability, algorithmic risk, and data ethics woven into every module.
- Case-Based Reasoning & Interview Preparation: regulatory case analysis, breach-response scenarios, and DPO-style judgment calls built into the curriculum, not left as an afterthought.
- Public Professional Record: graduate with a documented compliance framework, case-study portfolio, and professional record — verifiable evidence, not just a certificate.
- India-Specific Regulatory Coverage: the DPDP Act, India's Data Protection Board, and sector-specific rules (RBI, IRDAI, SEBI data-handling requirements).
- Designed for Busy Professionals: 24-week format with 1 class per week scheduled after working hours, allowing you to upskill without disrupting your career.
- Long-Term Access: 3 years of updated content and community access, so you stay current as tools and regulation evolve.
Can I get remote freelance work after doing this course?
Yes, Data protection and privacy work increasingly happens as independent, project-based engagements — DPO-as-a-service arrangements, privacy audits, and compliance advisory for organisations that don't have in-house capacity. The consulting and advisory focus of this program, particularly the Governance track and the Data Governance & Compliance Consultant career path, is built around the skills this kind of independent practice requires.
How will you clear my doubts and help me if I am struggling to understand or learn a concept?
In our live weekly classes, you can ask questions and have your doubts cleared directly. Beyond that, you have access to unlimited one-on-one doubt-clearing sessions with mentors and instructors — so if you're struggling with a concept after an assignment, or want tailored career advice, you can schedule a private call.
Faculty
Yash Vijayvargiya,
Co-Founder of Lawsikho & SkillArbitrage, Spearheading 100+ courses in AI, Law & Marketing to empower 25,000+ learners across the world

Abhishek Pareek,
Deputy Director, LawSikho and SkillArbitrage, Worked with more than 5000 professionals, transforming their careers remotely.

Aishvarya Joshi,
Senior Associate, at LawSikho / Skill Arbitrage. Legal Tech Consultant, leads Tech, Privacy-focused courses, and mentoring programs focused on global data protection laws, ISO standards, and AI governance frameworks. Known for her structured and practical approach, she empowers learners to apply privacy, compliance, and governance principles effectively across industries.
Syllabus
Module I: Introduction to Data Collection, Processing, Protection, and Transfer under EU GDPR 
 Why is data sought to be protected, and what are the different types of data? — Covers the rationale behind data protection and the classification of personal, sensitive, and special categories of dat
Are you a Data Controller or a Data Processor? — Explains how to identify your role in data handling and the distinct responsibilities attached to each.
Does the GDPR apply to you? — Covers the territorial and material scope of GDPR, including its extraterritorial reach over non-EU entities.
Rights of Data Subject — Examines the rights of individuals such as access, rectification, erasure, portability, and objection under GDPR.
The Obligation of a Data Controller and a Processor under GDPR — Details the compliance duties of controllers and processors, including lawful basis, security measures, and accountability.
Data commodification — under what conditions can you buy and sell data — Explores the legal limits and conditions under which personal data can be monetised or traded.
Cross-Border Transfer of Data — Covers mechanisms like adequacy decisions, SCCs, and BCRs for lawfully transferring data outside the EU.
Data Retention and Data Graveyards — Explains retention limits, storage limitation principles, and risks of holding obsolete or unused data.
What are the consequences of ignoring Data Protection Responsibilities — Covers penalties, fines, enforcement actions, and reputational risks of non-compliance.
How to conduct Legitimate Interest Assessment (LIA) — Teaches the three-part test (purpose, necessity, balancing) to rely on legitimate interest as a lawful basis.
How to Conduct a Data Protection Impact Assessment — Covers when a DPIA is mandatory and the step-by-step process of assessing high-risk processing.
AI governance: Introduces why AI systems need governing, the common risks such as bias and opacity, the risk categories under the EU AI Act, and the four functions of the NIST AI Risk Management Frame
Module II: Data Processing Agreement and Related Work Under GDPR
How to draft a Data Processing Agreement — Covers the mandatory clauses under Article 28 and practical drafting of controller-processor contracts.
How to Draft Privacy Policies so that they are compliant with the GDPR — Teaches drafting transparent, complete privacy notices meeting Articles 13 and 14 requirements.
How to Draft a Privacy and Cookie Policy — Covers cookie consent requirements, ePrivacy rules, and drafting compliant cookie banners and policies.
How to Implement Privacy by Design — Explains embedding data protection principles into products, systems, and processes from the design stage.
How to Conduct a Transfer Impact Assessment — Covers assessing destination-country laws and supplementary measures post-Schrems II before transferring data abroad.
Module III: Data Protection Practice in India
Indian Data Protection, DPDPA 2023 — Introduces the framework, key definitions, and obligations of Data Fiduciaries under the Digital Personal Data Protection Act, 2023.
Indian DPDPA Rules 2025 — Covers the operational details in the Rules, including consent notices, breach reporting, and Consent Manager provisions.
Implementation of Indian Data Protection Law — Focuses on practical compliance steps for businesses transitioning to the DPDPA regime.
Module IV: Privacy Law Compliance in the US
Federal data protection laws in the U.S. — Surveys sectoral federal laws such as HIPAA, GLBA, COPPA, and the FTC's role in privacy enforcement.
Important state data protection laws in the US — Covers key state statutes like those of Virginia, Colorado, Texas, and other comprehensive state privacy laws.
Data Protection Law in California — Examines the CCPA and CPRA, consumer rights, and business obligations under California's regime.
How to Comply with HIPAA Rules — Covers the Privacy, Security, and Breach Notification Rules applicable to protected health information.
How to handle DSRs in the US — Teaches processes for receiving, verifying, and responding to consumer data subject requests within statutory timelines.
How to prepare a gap report for US privacy laws — Covers auditing an organisation's practices against US privacy requirements and documenting compliance gaps.
Course Plan
Standard
₹ 155000
incl. of all charges
Instructor-led course with 1 live online class per week, plus 2 practical exercises weekly (Effort: 12–15 hours/week)
Practical, hands-on exercises with reviewed frameworks and projects — every week produces a portfolio artifact
Digital certificate, co-branded by SkillArbitrage and iHUB DivyaSampark, IIT Roorkee
Full digital access to study materials, on LMS, Android & iOS apps
Digital Learner Identity Card for program access and engagement
iHUB DivyaSampark, IIT Roorkee newsletter subscription
Unlimited doubt clearing — one-on-one sessions with mentors and instructors
Optional campus visit and networking session at the IIT Roorkee campus
3-year access to updated content and community